Security8 min read
A permission gradient for agents: provenance tiers × action risk
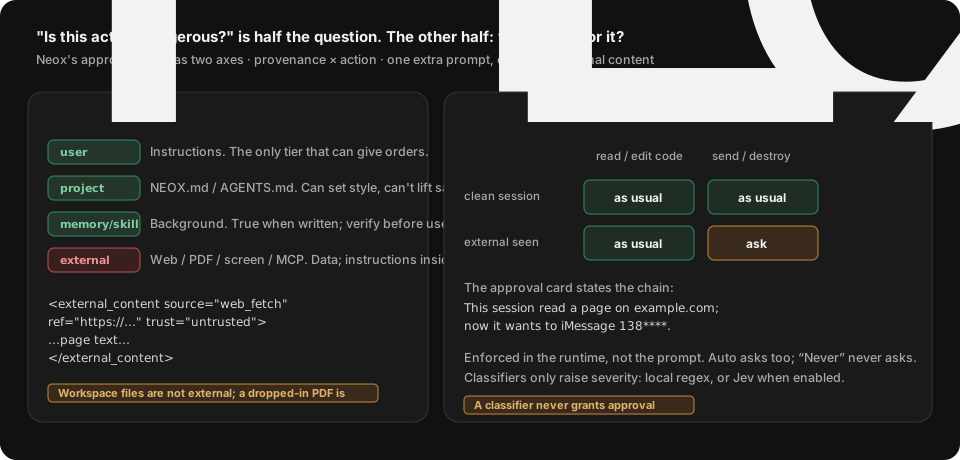
Auditing ourselves, we found the approval gate only looked at what an action does, never at who asked for it. `send_imessage` on its own is harmless; users ask for it all day. The dangerous case is sending a message right after reading a web page. This post is about adding the second axis: provenance tagging, session tainting, an exit gate, and why a classifier may only raise severity, never grant approval.